
Compiled By: Malami Haruna Dogon daji
OCTOBER 7, 2026 – ABUJA NIGERIA
Operating from the shadows with a trail of high-profile attacks spanning healthcare, transport, and government institutions across more than 60 countries, the Qilin ransomware group has cemented its status as one of the most prolific and destructive cybercrime syndicates in the digital age.
Anatomy of a Cyber Threat
Origins and Identity
Originally observed in July 2022 under the moniker “Agenda,” the group underwent a strategic rebrand to “Qilin” between August and September 2022 while retaining its core infrastructure and affiliate network. Threat-intelligence agencies and cybersecurity analysts widely attribute the operation to Russian-speaking actors, noting the group’s active recruitment and coordination within Russian-language underground forums.
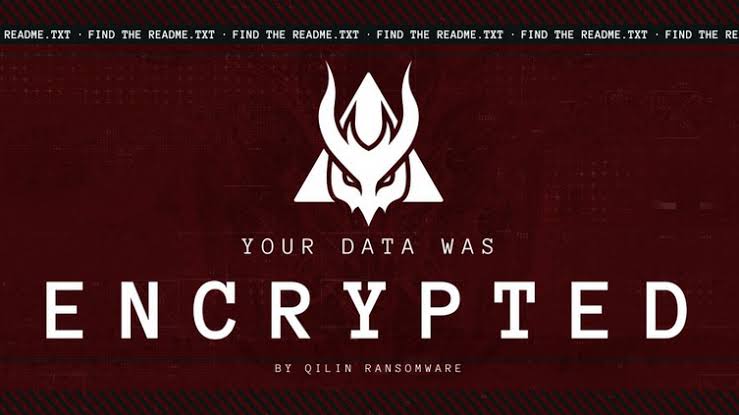
Operating on a Ransomware-as-a-Service (RaaS) model, Qilin develops malicious encryption tools, manages dark-web leak sites, and handles extortion negotiations while leasing its infrastructure to independent affiliates who execute the attacks and split the illicit proceeds.
Scale and Unprecedented Growth
The syndicate has experienced explosive growth in operational scale:
- Record Victim Numbers: Qilin claimed between 958 and 1,044 victims, emerging as the single most active ransomware group during that period.
- Surging Activity: Between April 2025 and March 2026, the group logged 1,358 victim claims—representing a staggering 443% year-over-year increase.
- Global Footprint: Over 330 victims are located in the United States, alongside significant concentrations in Canada, the United Kingdom, France, and Germany across a total of 62 countries.
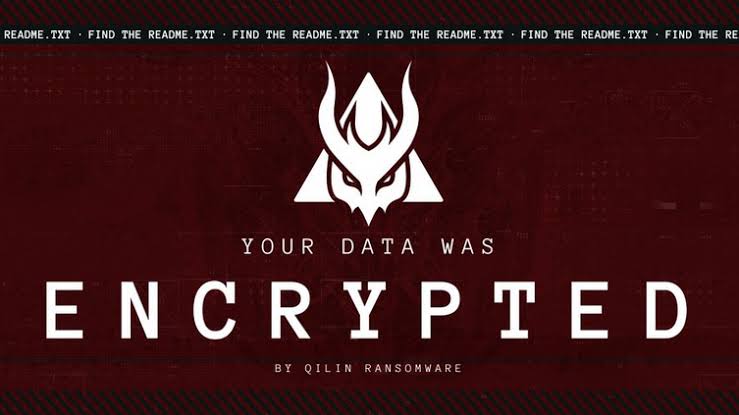
“Qilin’s willingness to strike critical infrastructure, healthcare providers, and public transport systems highlights the grave physical and economic risks modern ransomware poses to global security.”
Fast Facts: Qilin Ransomware Syndicate
- Initial Appearance: July 2022 (formerly known as “Agenda”)
- Operational Model: Ransomware-as-a-Service (RaaS)
- Estimated Lifetime Victims: Over 2,000 targeted entities
- Primary Targets: Manufacturing, healthcare, technology, financial services, and critical infrastructure
- Notable Incidents: Synnovis/NHS hospitals (UK), Asahi Group Holdings (Japan), and Malaysia Airports Holdings Berhad
Social Call-to-Action (CTA)
As cyber threats increasingly target essential public services and critical infrastructure, what measures can organizations and governments implement to build stronger digital resilience? Share your thoughts on NTA’s digital platforms @NTANetwork